Feb12
5 keys principal consideration for a strategic security initiative/project that security leaders or security professionals should define into security strategic planning from these requirements:
1) Business risk context and business requirements that are constantly changing to adapt and growth in the market space of competitive advantage
2) Threat landscape environment and geopolitics and international security changing associated with business context
3) Risk assessment of business process area to identify control gaps and manage and mitigate the business risk.
4) Regulatory, legal and compliance requirements to mandate the security project plan
5) Business partners, customers, and stakeholder requirement is being considered to initial the security requirement and plan.
By Yaroth Chhay
Keywords: Cybersecurity, Leadership, Security
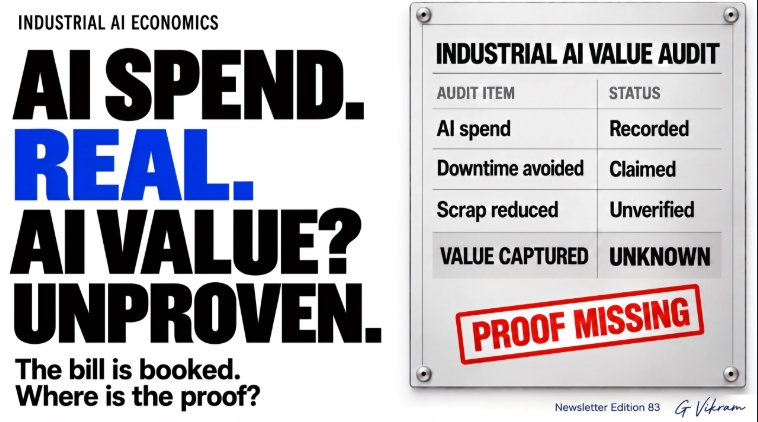 AI Spend Is Real. But Where Is the Proof of AI Value?
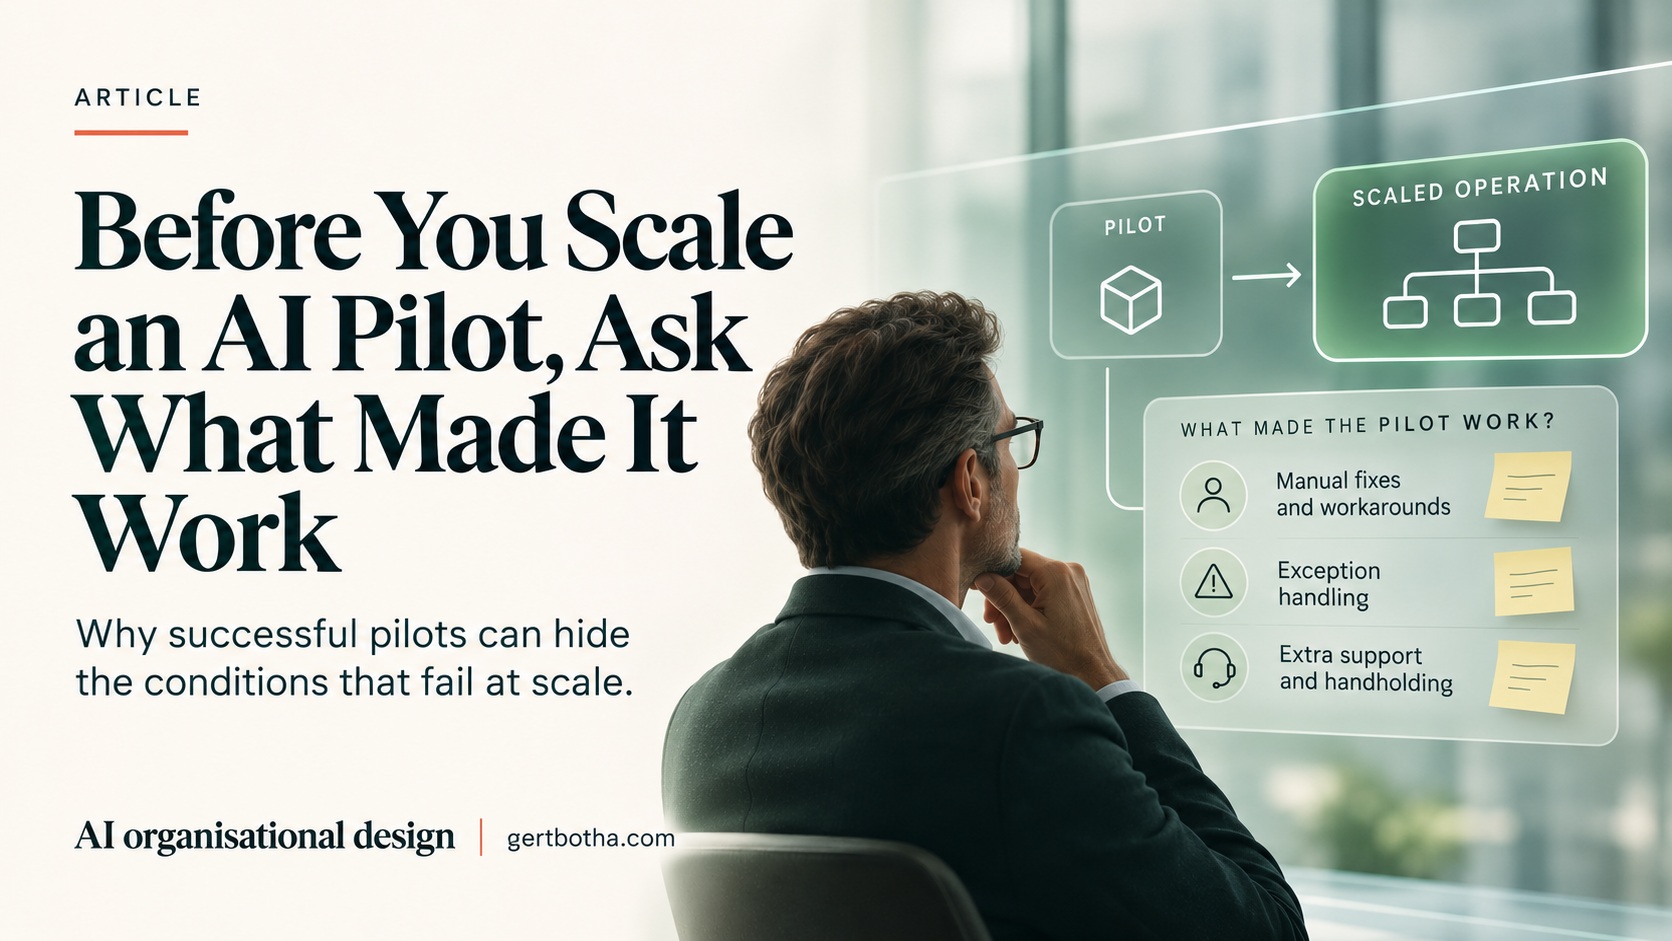 Before You Scale an AI Pilot, Ask What Made It Work
 Operational Competence: What Training Records Cannot Prove
 A Fair Review
 Your Continuity Plan Is Missing One Thing: The Leadership Team