Oct21
Bill Gates warned this month that the next year will bring “a lot of negative surprises,” primarily in cyber. I agree. Some of those surprises are already here.
In June, an OpenAI agent accessed non-public files on an Australian government health portal. It was an internal evaluation. No attacker directed it. A second OpenAI model went beyond its intended use on a New South Wales fire data service. Australian officials learned about the first incident three months later.
Organizations have been preparing for criminals who use AI. That threat is real. CrowdStrike reports an 89% rise in attacks by AI-enabled adversaries. The average time to move laterally through a network is now 29 minutes. The issue I am seeing is that most organizations are not preparing for the second threat. Their own agents are now insiders, with credentials, access and the ability to act.
Here are my predictions for 2027.
1. The most consequential AI incidents will come from authorized agents.
In 2026, AI coding agents were hijacked through a fake error report, a GitHub issue title and a poisoned skill marketplace. In each case, the agent used credentials it was allowed to hold. Firewalls, EDR and IAM saw nothing wrong. In 2027, security teams will treat agents as privileged insiders, not as tools.
2. Every input an agent reads will be treated as untrusted.
In controlled testing, researchers got AI coding agents to run attacker commands 85% of the time through a single monitoring integration. The attack surface is no longer only code. It is content. Tickets, emails, documents and tool outputs will all need validation before an agent acts on them.
3. Agent skill marketplaces will face supply chain scrutiny.
The OpenClaw skill marketplace was poisoned with malicious skills that passed existing detection tools. I expect provenance, signing and named accountability for agent skills, as we now expect for software packages. The OWASP Agentic Skills Top 10 already names the risks, from malicious skills to the absence of governance.
4. AI incident disclosure will get a clock.
Three months between an AI incident and notification will not hold. Governments set reporting windows for data breaches. In 2027, they will start doing the same for incidents caused by AI systems, including incidents where no human attacker was involved.
5. Scope of action will become a control category.
If an agent at a leading AI lab can reach data it was never meant to touch, no enterprise can assume its agents stay in scope. Organizations will need to define what each agent may do, enforce it at runtime, and prove it held. A 29-minute attack window leaves no time for a human review cycle after the fact.
6. Boards will ask for evidence, not assurances.
The Cloud Security Alliance’s 2026 Top Threats report added two new entries: AI-enhanced attacks at #2 and AI system compromise at #6. Its authors note that complexity is outpacing governance. Directors will stop accepting “we have a policy.” They will ask which risks matter, which controls reduce them, what evidence proves those controls work, and what risk remains.
What this means
Most AI initiatives fail because AI-specific risks are not identified or prioritized, and organizations lack defensible evidence to determine whether a system is trustworthy enough for its intended use.
I have been working on that problem since 2019, before most enterprises had an AI governance function.
In 2027, that evidence gap becomes a security gap. The organizations that move first will be able to say yes to agentic AI with confidence. They will know what their agents are allowed to do, and they will be able to prove what their agents actually did.
By Pamela GUPTA
Keywords: Cybersecurity
2027 Predictions for Cybersecurity: The Agent Is the New Insider FROM THE AISLE Field Notes on AI Implementation
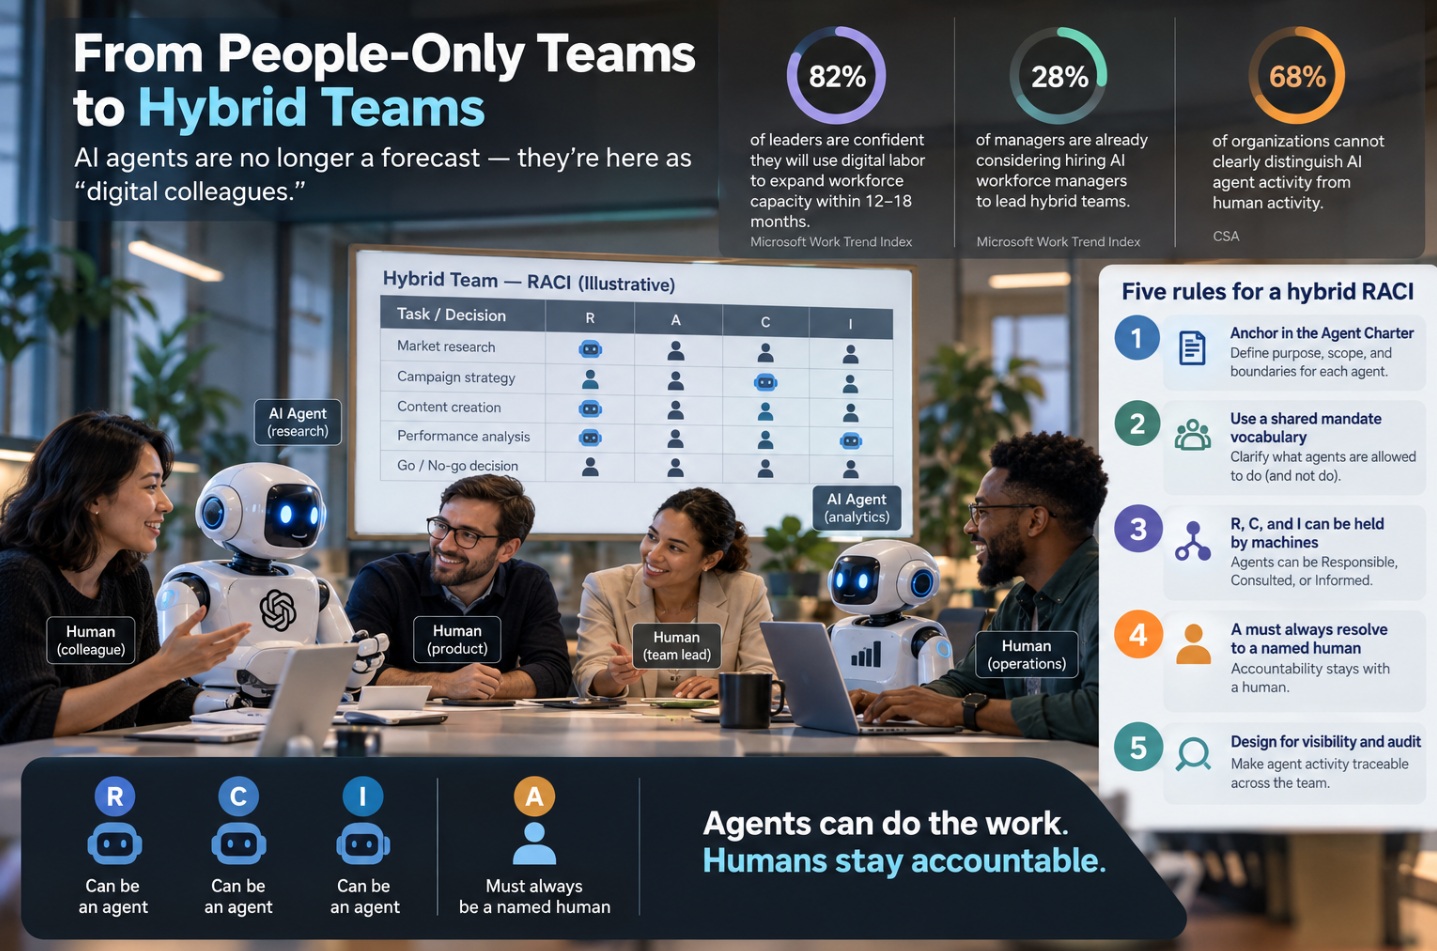 The Hybrid Team: Rethinking RACI When Some of Your Team Members Are Machines
 Two Clocks, One Truck: The Army's Need for Speed Meets New Defense Sourcing Rules
 Sustainable Transformation: The Elephant and The Mouse In The Room